Security That's Engineered In, Not Bolted On
Penetration testing, security audits, 24/7 threat monitoring, and compliance hardening — from the team with zero breaches across every property we've ever built or hosted.
Defense in Depth, Verified by Attack
Gleyon secures systems the way attackers approach them: by trying to break in. Our offensive testing feeds our defensive engineering — every finding becomes a hardening step, a detection rule, or a runbook, not a PDF that gathers dust.
Behind that sits a 24/7 monitored perimeter: WAF, intrusion detection, patch management, and an incident response team with rehearsed playbooks. Zero breaches since day one is not a slogan — it's the record we defend every day.
- Penetration testing of web apps, mobile apps, APIs, and infrastructure
- Security architecture reviews and hardening of existing systems
- 24/7 threat monitoring with intrusion detection and alerting
- Incident response with rehearsed playbooks and defined RTOs
- Compliance support — PCI-DSS, HIPAA, SOC 2, GDPR readiness
- Security training and phishing simulations for your team
Built for Teams Where a Breach Isn't an Option
Enterprise deals are stalling on SOC 2 or ISO 27001 security questionnaires — you need audit-ready answers, fast.
You handle regulated data under PCI-DSS or HIPAA, and "probably compliant" is a phrase you can't afford.
A phishing near-miss, a suspicious login, a competitor breached — you want to know your real exposure this quarter, not next year.
Annual pentests aren't enough anymore — you need continuous monitoring, detection, and a team that answers at 3 a.m.
Offense-Informed Defense
Penetration Testing
Manual, scenario-driven testing of apps, APIs, and networks — with proof-of-concept exploits and ranked fixes.
Managed Security Monitoring
24/7 SIEM-backed monitoring, intrusion detection, and alert triage by our NOC — minutes to response, not days.
Compliance & Audit Readiness
Gap assessments and control implementation for PCI-DSS, HIPAA, SOC 2, and GDPR — evidence included.
Application Security
Secure code review, dependency scanning, and secrets management wired into your CI/CD pipeline.
Incident Response
Contain, eradicate, recover: rehearsed playbooks, forensics, and stakeholder comms when minutes matter.
Cloud Security Hardening
Least-privilege IAM, network segmentation, encryption at rest and in transit across AWS, Azure, and GCP.
A Process You Can Set Your Watch To
Four stages, weekly demos, zero surprises. You always know what shipped, what's next, and what it costs.
Assess
Asset inventory, threat modeling, and a baseline audit — you get a ranked risk register, not a wall of CVEs.
Harden
Highest-risk gaps closed first: access control, patching, encryption, and network segmentation with change windows you approve.
Monitor
Detection rules, log aggregation, and 24/7 watch go live — every alert triaged by a human before it reaches you.
Respond & Improve
Incident playbooks rehearsed quarterly, findings fed back into hardening, and re-testing to prove fixes hold.
Three Ways to Work With Us
Know Where You Stand
A point-in-time offensive engagement that maps your real attack surface. Scoped proposal in 48 hours.
- Full penetration test with proof-of-concept exploits
- Ranked risk register — severity, impact, effort to fix
- Remediation plan your engineers can act on directly
- Cloud and application configuration review included
- Free re-test to verify every critical fix holds
Your 24/7 Security Team
Continuous monitoring, detection, and response on a monthly cadence. Scoped proposal in 48 hours.
- 24/7 SIEM-backed monitoring and alerting
- 15-minute critical response SLA, human-triaged
- Quarterly re-testing so fixes never quietly decay
- Patch management and vulnerability remediation
- Incident response with rehearsed playbooks included
Audit-Ready, Continuously
From gap assessment to passed audit for SOC 2, ISO 27001, PCI-DSS, or HIPAA. Scoped proposal in 48 hours.
- Gap assessment against your target framework
- Control implementation with your existing tools
- Audit-ready evidence collected continuously
- vCISO guidance for policies and vendor reviews
- We sit beside you through the audit itself
The Difference, Line by Line
| What matters | With Gleyon | Typical provider |
|---|---|---|
| Findings | Exploit proof plus concrete fix guidance | 200-page PDF of raw scanner output |
| Coverage | 24/7 monitoring, every day of the year | Annual checkbox audit, then silence |
| Response | 15-minute SLA on critical alerts | A ticket answered next business day |
| Remediation | We fix issues alongside your team | Report delivered, consultants disappear |
| Compliance | Evidence collected continuously, all year | Panic gathering the week before the audit |
| Scope | Applications, cloud, and people covered | A network scan and little else |
We passed SOC 2 on the first attempt because the evidence was already sitting there, collected all year. And their pentest findings came with fixes, not fear — every issue had a proof, a severity, and a path to done.
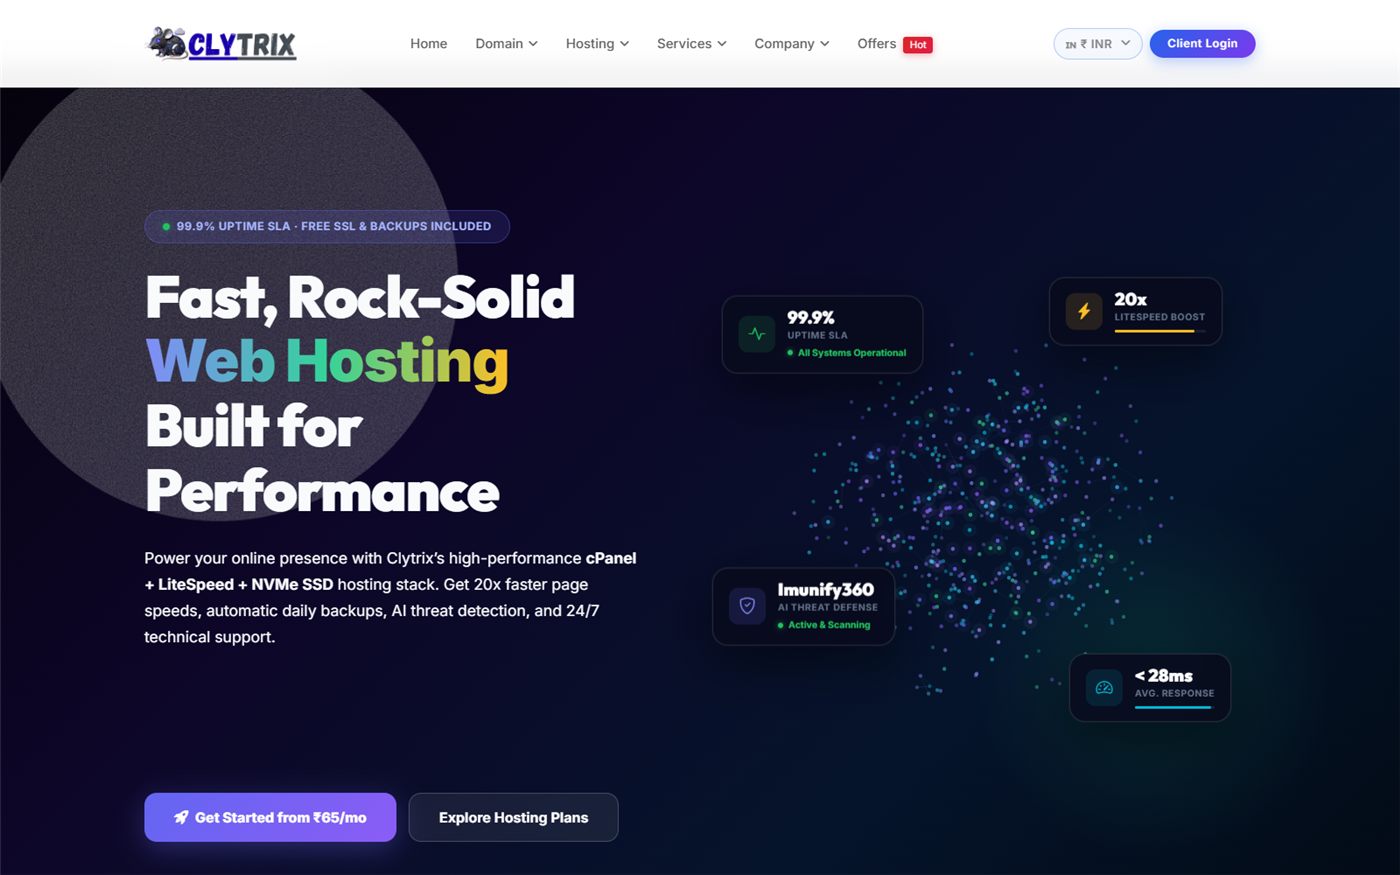
Security Work You Can Click Through
Cybersecurity Questions, Answered
How disruptive is a penetration test to our live systems?
We're a mid-size company — are we really a target?
Can you help us pass a compliance audit like SOC 2 or PCI-DSS?
What happens when you find something critical?
Do you work with our existing IT or engineering team?
Close the Loop Around Your Stack
Hardened, Gleyon-managed infrastructure with WAF, automatic SSL, and the same 24/7 NOC that watches your alerts.
Explore Cloud & DevOpsLeast-privilege IAM, encrypted pipelines, and infrastructure-as-code so security findings stay fixed in every deploy.
Explore AI & AutomationAutomated triage, anomaly detection, and workflow automation that make your security operations faster and cheaper.
ExploreFind Your Weaknesses Before Someone Else Does.
Start with a security assessment. We'll return a ranked risk register, a hardening plan, and a fixed price within 48 hours — no scare tactics, just findings.